Append-only decision records
An async REST and webhook API accepts inference event payloads: input hash, model id and version, output, confidence, timestamp, human override flag.
Waitlist open
Auditrek captures inference events out of band over REST and webhook, stores them as SHA-256 hash-chained append-only records, and generates structured documentation mapped to EU AI Act Article 12 and 13 fields.
A look inside
The problem
A supervisory authority asks what input your credit, hiring or triage model received on a given day, which model version scored it, what it returned, and whether a human overrode it. Most teams can assemble an answer from application logs and a data scientist's memory, and none of it is tamper-evident. Cloud platforms have a liability reason not to own decision accountability. Legacy GRC tools were built for process controls, not probabilistic inference. Experiment trackers were built for data scientists. Auditrek was built for the moment you have to hand over the record.
What it will do
For what it covers, see the pages this site publishes.
An async REST and webhook API accepts inference event payloads: input hash, model id and version, output, confidence, timestamp, human override flag.
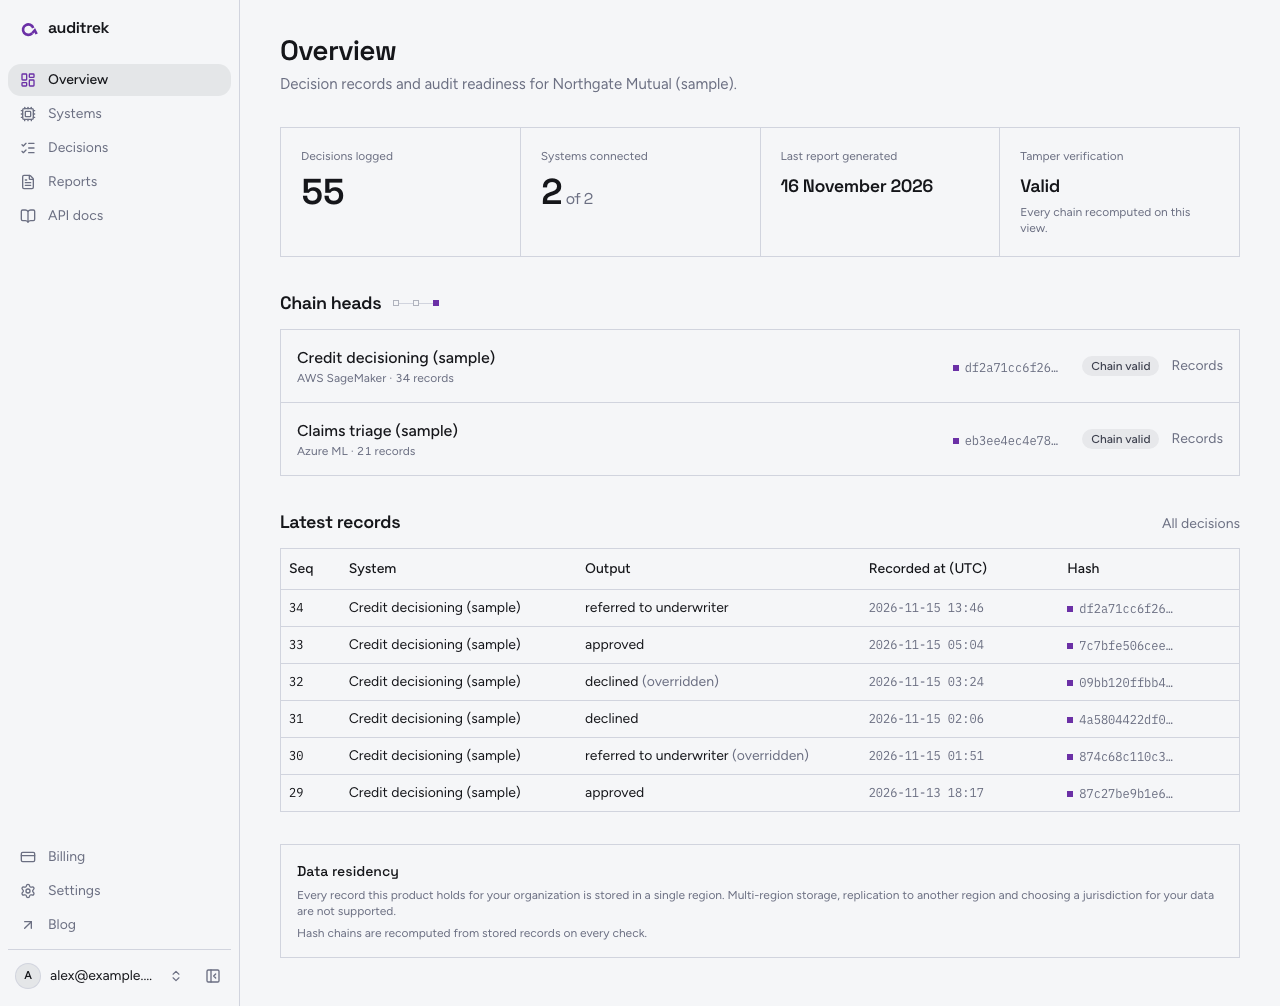
Decisions logged, systems connected, last report generated, and current tamper-verification status, written for a compliance officer rather than for the engineer who owns the pipeline.
A documented REST and webhook payload schema with field mapping guides for AWS SageMaker and Azure ML. No SDK to install in your pipeline and no bespoke platform agent, which is why nothing Auditrek does sits on the inference critical path.
How it will work
Add an AI system and record its data processing agreement confirmation. Until signed_at exists on that confirmation, the connect endpoint returns 403 and issues nothing.
With the DPA recorded, connecting the system issues an API key and a webhook secret scoped to that system. Store them in your secret manager.
Your pipeline posts input hash, model id and version, output, confidence, timestamp and human override flag to the REST endpoint or fires the webhook.
Each accepted record takes the next sequence number and a hash computed from the previous record. Run verification on any record and the server recomputes the chain from sequence 1 and tells you where it breaks, if it does.
Pick a system and a period, and Auditrek renders PDF and HTML output structured against EU AI Act Article 12 and 13 fields, disclaimer included, ready to hand to counsel or an auditor for their own assessment.
Who it is for
For who it covers, see the pages under Who it is for.
Compliance officers in financial services
Automated scoring runs thousands of times a day and the record of each run lives in application logs nobody designed for examination. Auditrek gives each decision a sequence number, a hash and a date-range report you can produce without a data engineer.
AI governance leads in insurance
When a model version changes mid-quarter, the question becomes which version scored which case. Records carry model id and version at capture time, so the answer is in the ledger rather than in a deployment log.
Compliance and clinical informatics in healthcare
The human override flag is a first-class field, so the record shows where a clinician disagreed with the model. The ingestion gate rejects diagnosis code patterns outright, keeping raw clinical data out of the ledger.
Senior ML engineers who own the pipeline
You approve the integration before procurement gets involved. Generic REST and webhook ingestion, documented payload mapping for SageMaker and Azure ML, async by design, no SDK in your serving code.
Questions
No, and we will not say otherwise. Auditrek produces structured records and documentation designed to support Article 12 and 13 record-keeping and transparency obligations. Whether your programme satisfies those obligations is a determination for your own counsel and your supervisory authority. Every report we generate carries a footer stating that the output does not constitute legal advice and has not been reviewed by qualified regulatory counsel.
No. Ingestion is async and out of band, over REST or webhook. Inline critical-path middleware is explicitly out of scope, so an outage or slow response on our side does not stall a production prediction.
No. Auditrek takes an inference event payload over a documented generic REST and webhook schema, with field mapping guides for AWS SageMaker and Azure ML. There is no SDK to embed and no bespoke platform agent at launch.
Each decision record is written with a sequence number and the previous record's hash, and the stored hash is sha256(prev_hash + payload), all committed atomically. Verification recomputes the chain from the first record rather than trusting a stored status field.
The ingestion API inspects payloads for recognisable raw sensitive-field patterns, such as SSN formats, ICD-10 style diagnosis codes and unredacted credit bureau fields, and rejects them with a 422 before anything is written. Subject identifiers are pseudonymised by default. Sending a raw sensitive field into the ledger is contractually prohibited unless you have confirmed your own lawful basis.
No. A countersigned data processing agreement confirmation with a signed_at timestamp must be recorded before any API key or webhook secret is issued, and that check runs server-side on the connect endpoint.
One template, EU AI Act Article 12 and 13 fields, rendered as PDF and HTML. EEOC and HIPAA templates and custom report builders are out of scope until the first template has been exercised with real customers.
Auditrek is pre-launch. Joining puts you in the first pilot cohort conversation, where we walk through the payload schema, the verification endpoint and a sample report against your own pipeline before anything is connected. No pipeline is connected without a countersigned DPA.
Leave your work email and we will send the payload schema, the verification endpoint documentation and a sample Article 12 and 13 report before you talk to anyone. Pilot cohort conversations start with your own pipeline, not a demo script.
One email when it launches, and one now to confirm your address. Unsubscribe any time. Privacy.